SECURONIX SECURITY FOR AI

Faster AI Defense. Controlled Cost.

AI is already touching sensitive data, production systems, and privileged workflows. Securonix helps security teams detect AI-related risk, connect it to enterprise evidence, and take approved action inside the SOC workflows they already use.

No separate AI security silo. No disconnected investigation path. No open-ended data bill.

Behavior-first detection. Decision-ready evidence. Human-owned action.
AI Risk Reaches Beyond the Model

Most AI incidents do not arrive as obvious “AI attacks.” They appear as familiar signals scattered across identity, cloud, data, endpoint, application, and network activity.

Securonix connects those signals so analysts can understand what changed, who or what was involved, and whether the activity creates real risk.

  • An employee using an unsanctioned AI tool with sensitive data
  • An approved agent calling an unfamiliar API
  • An administrator changing a guardrail or control-plane setting
  • A script moving more data than expected after AI service activity
  • A workload using valid permissions in an unusual way

The model may be secure. The environment around it can still expose the business.

Security for AI Without Another Security Silo

Securonix brings AI-related activity into Unified Defense SIEM, where analysts can investigate it alongside identity, data, device, cloud, endpoint, network, and threat intelligence evidence.

See What Rules Alone Miss

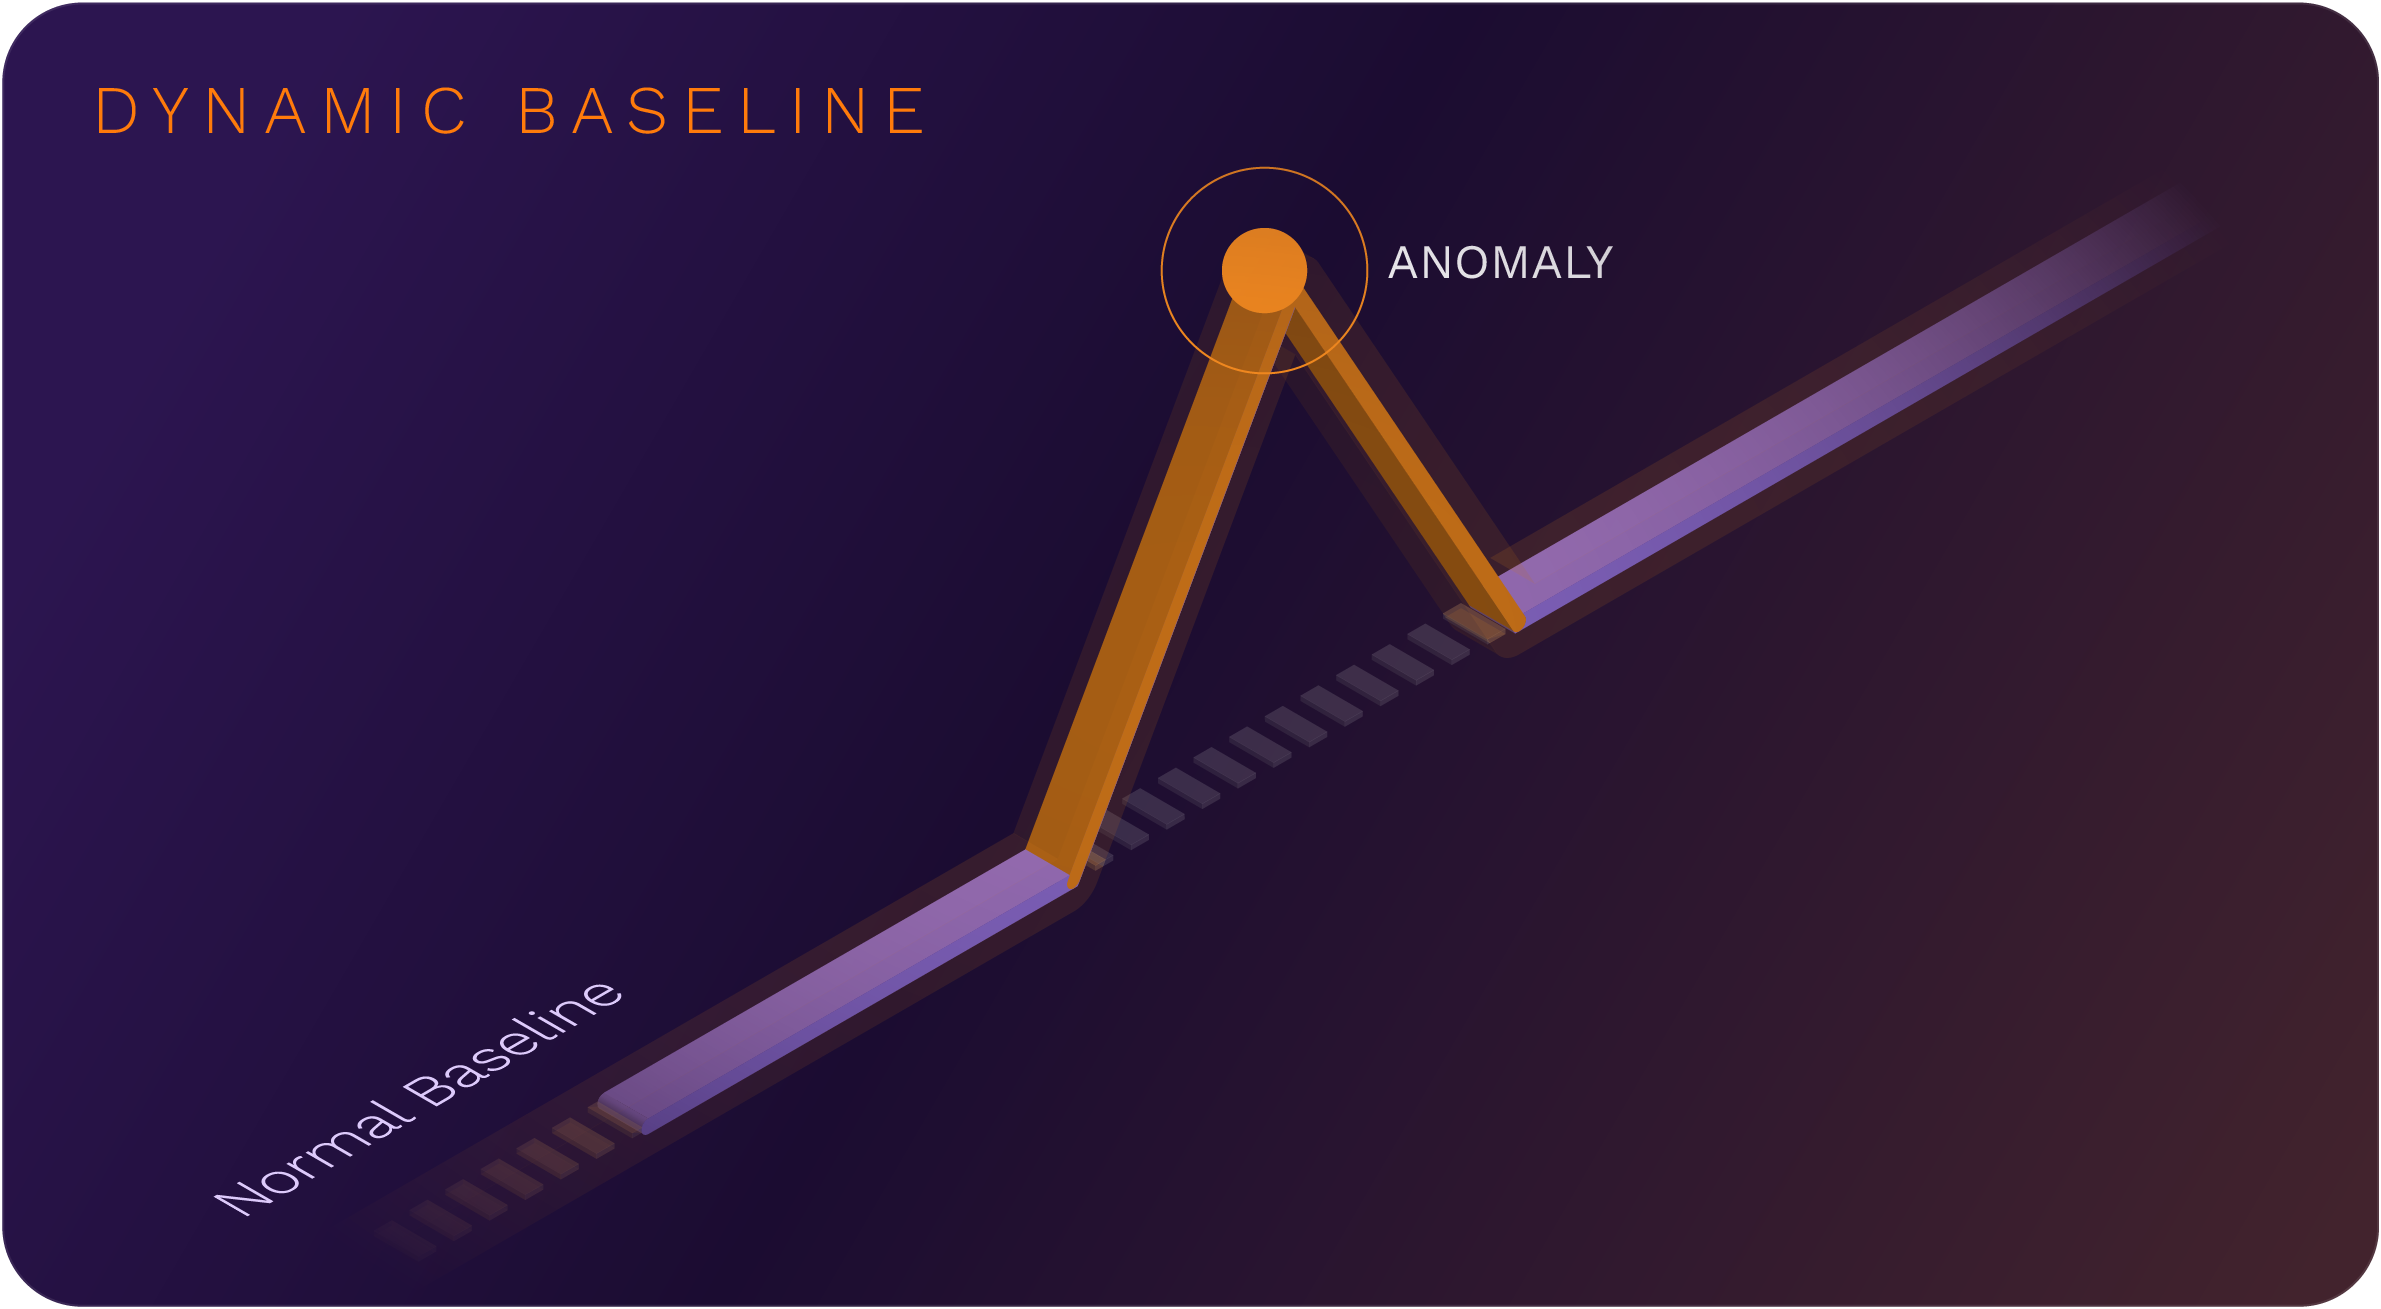
UEBA and Agent and Entity Behavior Analytics help identify when a user, identity, workload, or AI agent does something technically allowed but operationally unusual.

Build the Full Risk Story

Securonix connects AI activity to authority, data movement, devices, applications, network activity, and enterprise context across systems and time.

Move Faster with Control

Sam accelerates repeatable SOC work. Response Agent and SOAR support approved playbooks. Analysts retain authority over consequential decisions.

Keep Coverage Cost-Aware

Data Pipeline Agent routes and governs telemetry by purpose and value, helping teams manage the data costs associated with AI threat coverage.

Connected Threat Detection for AI

Enterprise AI relies on identities, permissions, data flows, endpoints, applications, infrastructure, and network paths. Securonix follows risk across that larger attack surface with 43 out-of-the-box policies across six AI threat domains. Coverage expands every two weeks as services and threats change.

Qualification: Availability depends on supported services, licensing, connectors, enabled logs, parsing, and required fields.

Turn Abnormal Behavior into Actionable Decisions

AI risk should move through the same evidence, investigation, and governance model your SOC already uses. Securonix helps teams collect activity, apply coverage, baseline behavior, build a case, and act through approved workflows.

  • Collect the right evidence: Bring in relevant activity from AI services, identity, cloud, data security, endpoints, applications, proxies, and firewalls. Validate logs and fields before relying on a detection.
  • Apply coverage that fits: Map out-of-the-box policies to the services and telemetry available in your environment.
  • Learn normal behavior: Baseline users, workloads, identities, and agents so legitimate adoption does not create unnecessary noise.
  • Build the case: Correlate identity, authority, data, endpoint, cloud, network, and threat intelligence into a clear investigation timeline.
  • Act inside defined controls: Use approved Response Agent and SOAR playbooks with clear ownership, human review, and an audit trail.

Permission Is Not Intent

An AI agent can use valid credentials and still act outside its purpose.

Securonix Agent and Entity Behavior Analytics looks beyond access rights to understand how the agent behaves. It evaluates expected purpose, authority, tools, data access, timing, volume, velocity, and sequence to help analysts identify drift, misuse, manipulation, or compromise.

The key question becomes simple: Which agent acted, whose authority did it use, and did the action make sense?

Governed Response for AI Risk

Securonix helps teams respond faster without handing over control.

Sam advances repeatable Tier 1 and Tier 2 work. Response Agent and SOAR support approved playbooks. Your policies define what AI may do, when a person must approve it, and who owns the outcome.

Accountability stays visible through evidence, reasoning, analyst decisions, approvals, and response history.

  • Policy aligned, with risk thresholds, privacy rules, approval paths, and separation of duties
  • Human supervised, with analysts able to approve, modify, override, or stop consequential actions
  • Explainable, with evidence and workflow details behind AI-supported recommendations
  • Auditable, with investigation history, ownership, approvals, and response evidence retained

Start with Usable Evidence

Good AI security begins with telemetry the SOC can trust.

Securonix helps teams turn existing data into durable AI threat coverage, then expand with confidence as services, agents, and use cases grow.

  • Confirm relevant AI, identity, cloud, data, endpoint, application, and network logs are enabled and stable
  • Match each detection to its required sources and fields
  • Baseline new services and agents before treating every first-time action as an incident
  • Define privacy, policy, approval, ownership, and audit rules before automating response
  • Measure the time from meaningful change to a decision-ready case, not only alert volume

Operational Outcomes

Securonix helps security teams improve AI threat detection while keeping investigation, response, and data cost under control.

Customers using related Securonix capabilities have reported:

Results may vary based on customer environment, configuration, data sources, deployment, usage, and other factors.

Security for AI: FAQ

Explore Security for AI resources

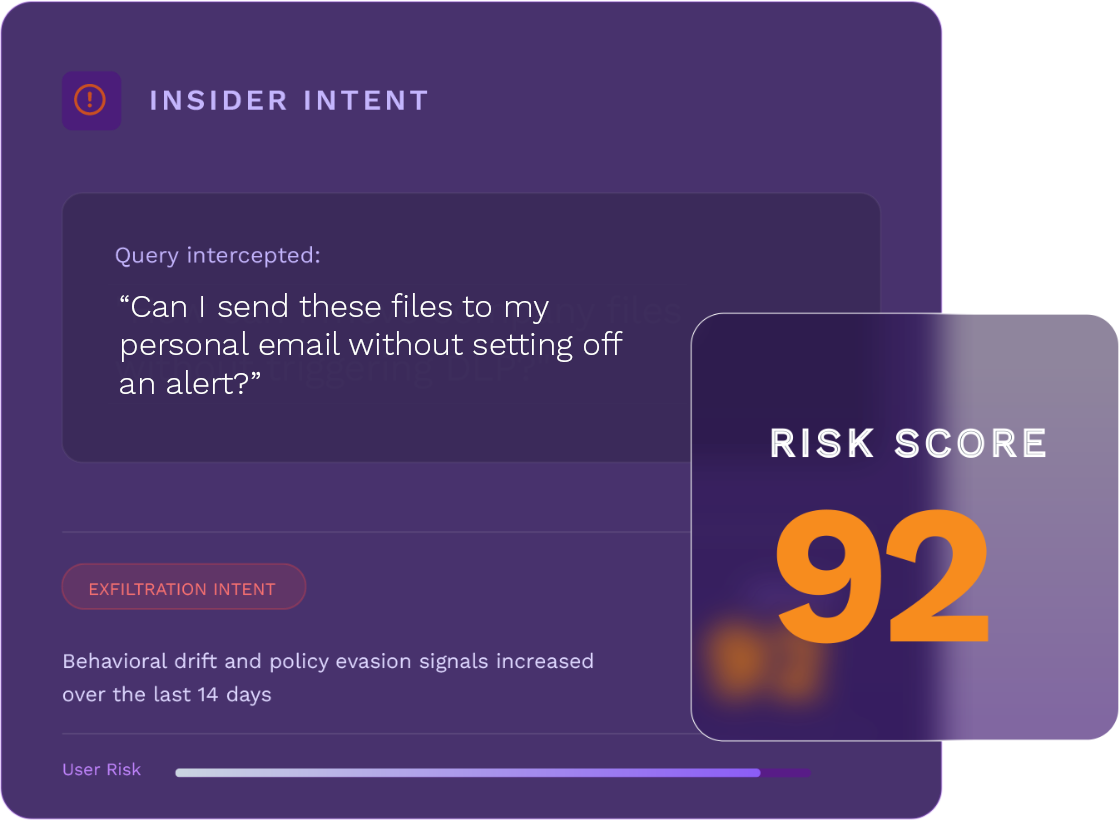
Go deeper on behavior-driven analytics, insider intent, AI-agent risk, SOC modernization, and AI threat analytics.

Ready to See It Live?

Make AI Risk Part of the Security Story 

Securonix brings Security for AI into Unified Defense SIEM so your SOC can detect meaningful change sooner, investigate with context, and respond with speed, oversight, and cost control.