Securonix Threat Labs

Get up-to-date threat content from the experts at Securonix Threat Labs.
Uncover the threats of tomorrow, today.

Securonix Threat Labs helps your team fend off rising threats by bringing the industry’s brightest minds together to equip you with the latest countermeasures and best practices.
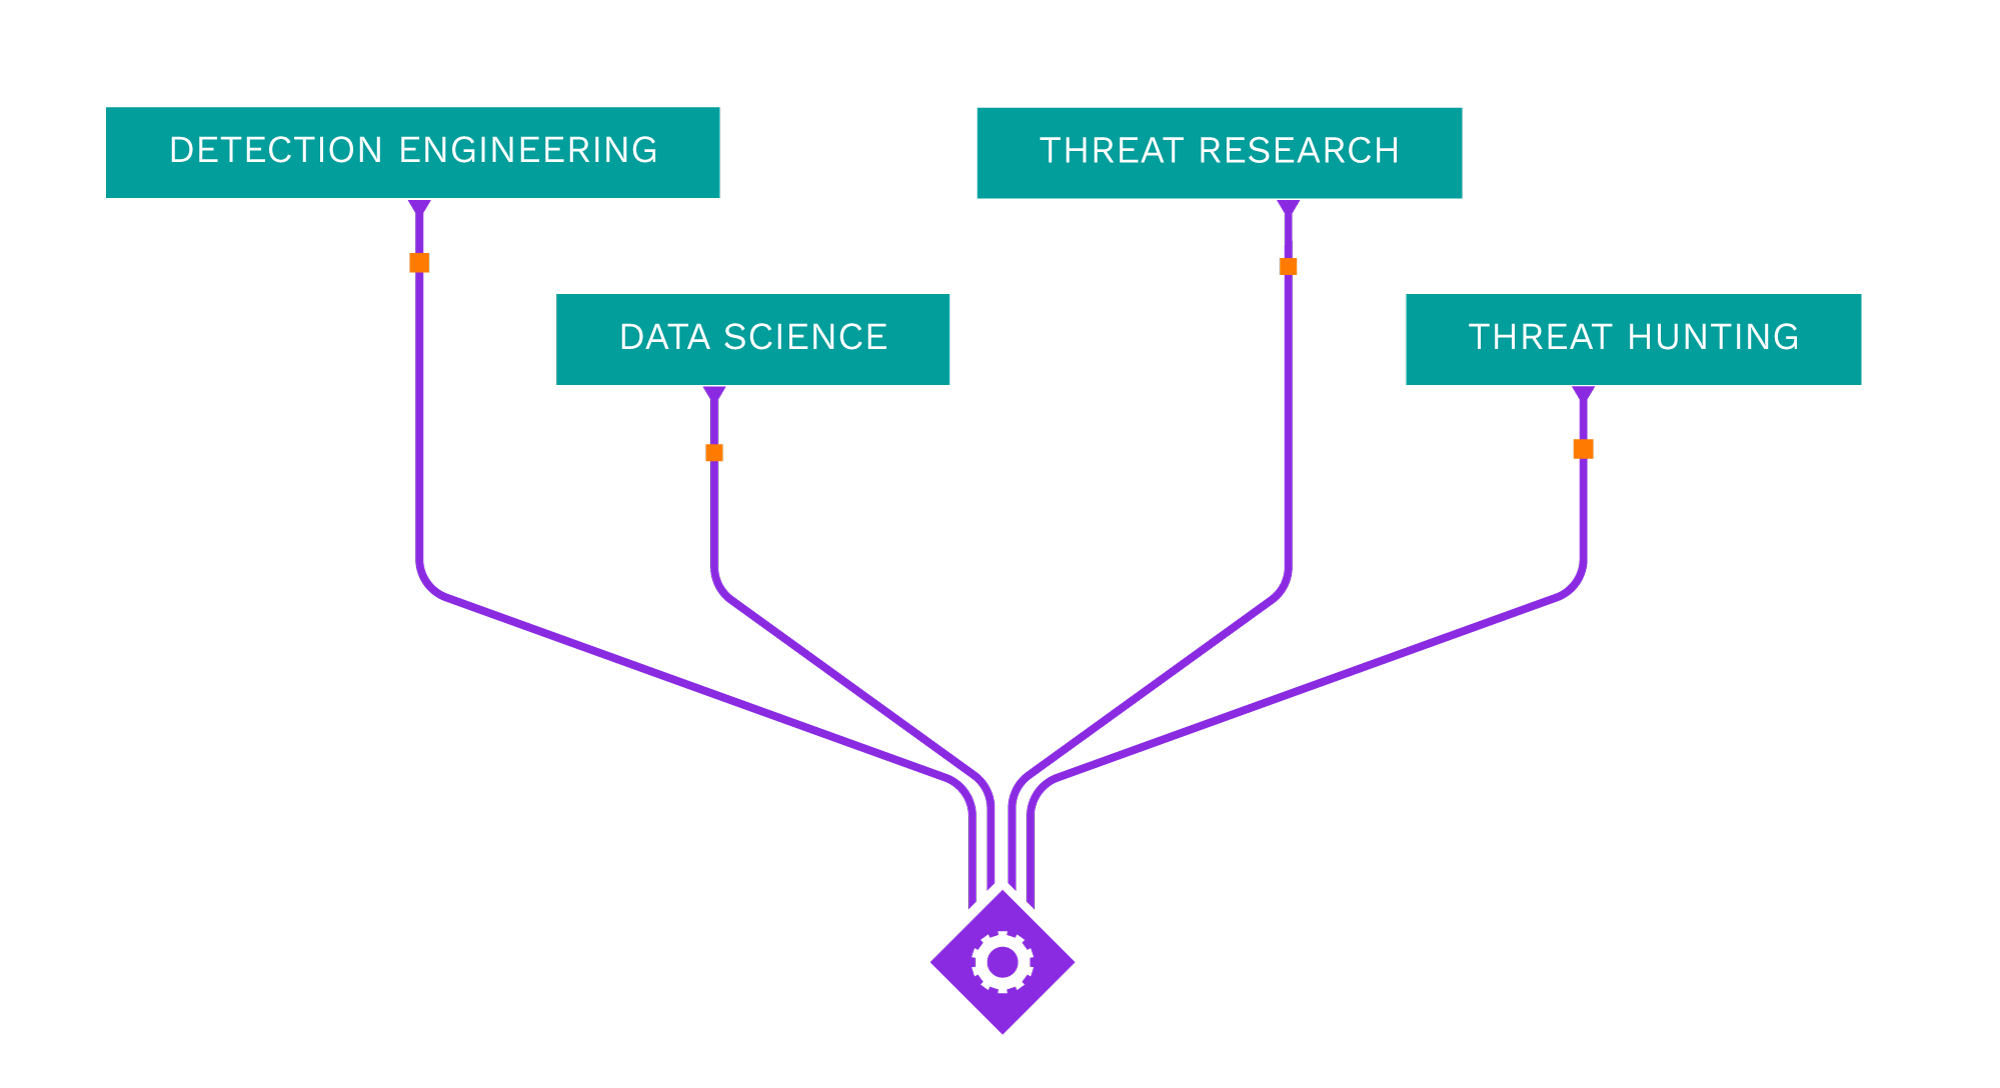
four prong diagram about detection, data, and threat research and hunting
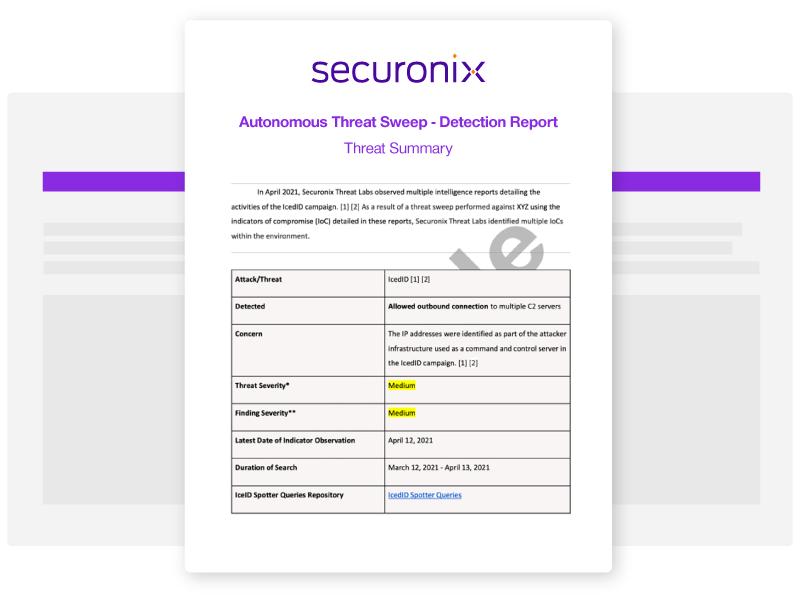
securonix autonomous threat sweep detection report sample

Powered by Threat Labs

Autonomous Threat Sweeper

Acting as your own dedicated Cyber Rapid Response Team, Securonix Autonomous Threat Sweeper (ATS) automatically and retroactively hunts for new and emerging threats based on the latest threat intelligence from our Threat Labs Team.

Latest ATS Entries

All indicators of compromise (IOC) and search queries are available on our GitHub repository.

10/29/26
n0n Credential-Driven Destructive Extortion
CRITICAL
+ —
Intel Source:
SOCRadar
Intel Name:
n0n Credential-Driven Destructive Extortion
Date of Scan:
10/29/26
Impact:
CRITICAL
Summary:
The n0n operation combined credential theft, data exfiltration, encryption, and deliberate deletion of enterprise data and backups. SOCRadar recovered an exposed operator workspace containing 1,719 files, including attack scripts and encryptor source code, that implicated 23 organizations across 14 countries. The publisher distinguishes 15 organizations subsequently published on the leak site, four compromised organizations not published, and four targets with access attempts but no demonstrated outcome. Documented entry routes used weak or stolen credentials, including FortiGate credential stuffing, exposed AWS keys, remote administration credentials, and reused hosting sessions; the recovered evidence did not establish vulnerability exploitation. At a sports retailer, an exposed cloud key enabled collection from 40 storage buckets and destructive deletion. Other cases involved theft of hosting backups and manipulation of an ISP's firewall policies. The operator claimed extensive network disruption, but that claim should remain separate from the documented policy changes. External scripts stopped services and removed recovery options before encryption, making recovery depend on backups outside the compromised administration plane. AI tooling helped produce and debug scripts, while the evidence supports a human-directed operation. Prioritize phishing-resistant authentication and revocation of exposed credentials across remote access and management portals. Restrict firewall policy administration and cloud deletion privileges, and investigate unusual token creation and bulk storage operations. Preserve independent, immutable backups and correlate endpoint, cloud, and firewall evidence during response.
Source: https://socradar.io/blog/n0n-ransomware-ai-assisted-extortion/
10/29/26
KeyDrift Intrusions into Cisco SD-WAN Controllers
HIGH
+ —
Intel Source:
Cisco Talos
Intel Name:
KeyDrift Intrusions into Cisco SD-WAN Controllers
Date of Scan:
10/29/26
Impact:
HIGH
Summary:
UAT-11473 exploited CVE-2026-20127 to gain unauthorized access to Cisco Catalyst SD-WAN controllers and installed the KeyDrift framework inside their control-plane environment. Cisco Talos reports targeting of space and satellite services, defense and aerospace technology, and policy research. Its October 28 analysis documents persistent controller access and collection mechanisms, although the activity described is historical and does not establish that every affected deployment remains compromised. The PolyFlame component enters legitimate controller processes through modified service launchers and process injection. It intercepts socket and encrypted control-channel operations, supports file access and command execution, and can relay commands between the operator and other peers. This placement gives the framework access to sensitive state inside trusted network-control processes. LittleFilch separately hooks decrypted control traffic, extracts session identifiers and what Talos assesses to be data-plane keying material, then encrypts collected records for staging or transmission. Talos could not recover its runtime destination configuration, and the exact in-band tasking format remains unresolved. The publisher assesses substantial infrastructure overlap with Volt Typhoon's covert access network with high confidence; the overlap does not resolve attribution of all the activity. Apply Cisco's controller patches and deployment hardening guidance first. Review service launchers, injected modules, and staging artifacts against the report's findings. Activate incident response and engage Cisco support when post-compromise evidence appears, because patching alone does not establish controller integrity.
Source: https://blog.talosintelligence.com/uat-11473-keydrift/
10/29/26
Doorway Botnet Compromises Network Devices and Java Servers
HIGH
+ —
Intel Source:
CloudSEK
Intel Name:
Doorway Botnet Compromises Network Devices and Java Servers
Date of Scan:
10/29/26
Impact:
HIGH
Summary:
The Doorway operation compromised routers, cameras, and exposed enterprise services to build a remotely accessible device fleet and proxy infrastructure. CloudSEK identified two identical exposed workspaces in October containing approximately 41 GB of operational material, including a Rust exploitation engine, 59 exploit modules, credential records, and execution evidence. The publisher observed the operation as active during its investigation. Evidence includes 7,369 successful RouterOS authentications across 4,923 device identities, 20 Jenkins hosts with confirmed remote code execution, and 16 Openfire plugin uploads. These measures represent different outcomes and should not be summed as unique compromised systems. An operator ledger reports substantially larger join and download totals, but downloads and repeated join events do not independently prove successful execution. The framework fingerprints services before selecting attacks, reuses default or exposed credentials, and supports multiple delivery methods and processor architectures. Payload retrieval can be signed and bound to the target address, while beacon evidence helps distinguish code execution from file delivery. Recovered components include a reverse shell and server-specific loaders. The final clients' full command protocol, some RouterOS exploitation outcomes, and commercial monetization remain unconfirmed. First restrict exposed management interfaces, rotate shared device credentials, and patch or isolate affected Java services. Then use the published indicators and detection rules to investigate delivery traffic, beacons, unexpected proxy settings, and unauthorized plugins. Preserve configuration history and network logs, and classify confirmed execution separately from probes and downloads.
Source: https://www.cloudsek.com/blog/doorway-botnet-global-iot-router-camera-enterprise-server-attacks
10/29/26
LiteLLM 1.107.0 Supply-Chain Credential Theft
HIGH
+ —
Intel Source:
ThreatMon
Intel Name:
LiteLLM 1.107.0 Supply-Chain Credential Theft
Date of Scan:
10/29/26
Impact:
HIGH
Summary:
The compromised LiteLLM 1.107.0 release placed credential-stealing startup hooks into Python environments reached through official package and container distribution. ThreatMon's October 28 research describes its inspection of the trojanized wheels and explains why exposure extends beyond applications that explicitly import LiteLLM. Installed startup files sit at the environment level, so an ordinary Python invocation can launch collection on a developer workstation, build runner, test container, or gateway host. The report traces release-pipeline takeover to stolen maintainer credentials and a workflow redirected to a lookalike repository, with a second compromised account used for deployment approval. The collector reads developer and AI-tool authentication data, cloud credentials, browser stores, private keys, process environments, and accessible application database fields. It encrypts collected data and attempts upload to an attacker-controlled service. Startup execution alone does not establish successful collection or exfiltration; response teams must assess each environment. A separate Unix loader can retrieve and execute additional Python code, but ThreatMon had not observed that component serving payloads in the wild. The malicious release was quarantined and affected container images removed, which does not remediate environments that already installed them. Identify and isolate systems that obtained the release, using inspection methods that do not start Python inside a suspect environment. Rebuild affected environments from trusted images and terminate surviving malicious processes. Rotate accessible credentials and audit their subsequent use across cloud, source-control, registry, and application services.
Source: https://threatmon.io/litellm-1-107-0-from-startup-hooks-to-credential-theft/
10/29/26
Help Desk Vishing Targets Canadian Enterprise Identities
HIGH
+ —
Intel Source:
Canadian Centre for Cyber Security
Intel Name:
Help Desk Vishing Targets Canadian Enterprise Identities
Date of Scan:
10/29/26
Impact:
HIGH
Summary:
Help desk impersonators are targeting Canadian organizations with voice phishing that relays authentication through fraudulent sign-in pages and can yield authenticated enterprise sessions. The Canadian Centre for Cyber Security's October 28 alert identifies targeting across multiple firms, with finance and legal organizations increasingly targeted since July and October activity concentrated on the legal sector. Callers claim that employees must urgently migrate passkeys, enroll authentication methods, or change passwords. They contact personal or office phones and collaboration services, sometimes spoofing support numbers or referencing internal personnel. Organization-branded phishing pages relay credentials and multi-factor responses to legitimate identity providers, allowing conventional multi-factor authentication to be bypassed through real-time interception. The alert includes concrete campaign-associated domains and notes frequent infrastructure rotation. Reported post-compromise behavior includes registration of attacker-controlled authentication methods, deletion of security notifications, password resets for applications outside single sign-on, and automated access to Microsoft 365 and connected services. Data theft can lead to extortion. The Cyber Centre attributes parts of that post-compromise account to cited reporting; it does not publish a victim count or establish that every targeted Canadian firm suffered those outcomes. Prioritize phishing-resistant authentication, managed-device access policies, and independent verification of unexpected support calls. Monitor authentication-method changes, security-mail deletion, and unusual bulk file access. If compromise is suspected, revoke sessions and tokens, remove unauthorized methods, reset affected credentials, and preserve identity and Microsoft 365 audit logs.
Source: https://www.cyber.gc.ca/en/alerts-advisories/al26-028-ongoing-help-desk-voice-phishing-campaign-targeting-canadian-organizations
10/29/26
Node2Shell Exploitation Attempts Against Brotli Decoders
MEDIUM-HIGH
+ —
Intel Source:
Zscaler
Intel Name:
Node2Shell Exploitation Attempts Against Brotli Decoders
Date of Scan:
10/29/26
Impact:
MEDIUM-HIGH
Summary:
Attackers probed and attempted to exploit vulnerable Brotli decoders shortly after disclosure of CVE-2026-111497, also called Node2Shell or HTTP2Shell. Zscaler ThreatLabz recorded 402 events from 20 source addresses targeting decoys associated with 12 customers during the first 24 hours. The report classifies 40% as reconnaissance and 60% as exploitation attempts, and provides activity-linked network indicators and fingerprints. These observations document hostile activity against exposed decoys. Zscaler does not confirm compromise of customer production systems. The vulnerability affects block-decoding logic and can produce an out-of-bounds write when malformed compressed data reaches a vulnerable implementation. Potential consequences include crashes, memory disclosure, and remote code execution, with actual exposure depending on application behavior and the bundled decoder. Affected paths include servers decompressing incoming requests and clients processing responses from external or user-controlled services. Node runtimes, Python bindings, service proxies, and other products can carry separate vulnerable copies, so a host-level library update may leave workloads exposed. The report references code execution demonstrated elsewhere in a test environment; that result should not be presented as an observed production intrusion. Prioritize updates for components that decompress untrusted data and rebuild affected containers with patched dependencies. Where updates are delayed, disable vulnerable decoding paths where supported and tested. Investigate malformed compressed traffic, correlated worker crashes, unexpected child processes, and subsequent outbound connections using the report's activity evidence.
Source: https://www.zscaler.com/blogs/security-research/cve-2026-111497-node2shell-http2shell-vulnerability-may-allow-rce
10/29/26
INJ3CTOR3 FreePBX Campaign Adds Credential Exfiltration
MEDIUM-HIGH
+ —
Intel Source:
Cyble
Intel Name:
INJ3CTOR3 FreePBX Campaign Adds Credential Exfiltration
Date of Scan:
10/29/26
Impact:
MEDIUM-HIGH
Summary:
INJ3CTOR3's JOMANGY campaign now includes repeated collection of telephone-system credentials, extending toll-fraud exposure beyond the infected PBX. Cyble compared earlier campaign artifacts with material collected from two operator staging hosts in September 2026. The updated installer contains commands to upload 17 configuration files covering SIP trunks, extensions, management access, databases, and mail relays. Recurring scheduled execution can repeat that collection every minute. Cyble observed the upload implementation in recovered code, rather than capturing an actual transfer, and it holds no victim list for this update. The report does not measure how many credentials reached the operator. The existing self-repairing persistence remains largely intact, while watermarks, access-gate values, and staging identifiers have changed. Encoded requests and rewritten web-server rules can reach a backdoor without naming it in access logs. Lab validation also showed why the management console can miss configuration written directly into the underlying telephone service. The staging servers stopped responding in late September, but their disappearance does not revoke previously exposed secrets. Isolate suspected systems and preserve scheduled tasks, account records, configurations, and carrier logs before remediation. Rebuild from a clean image or remove persistence from the system layer upward, then rotate every affected secret after the host is clean. Coordinate carrier restrictions, registration monitoring, destination controls, and spending limits to contain fraud using stolen trunk credentials.
Source: https://cyble.com/blog/hijacked-pbx-to-stolen-trunk-inj3ctor3s-campaign/
10/29/26
Fake DocuSign Installer Establishes Hexnode Persistence
MEDIUM-HIGH
+ —
Intel Source:
Huntress
Intel Name:
Fake DocuSign Installer Establishes Hexnode Persistence
Date of Scan:
10/29/26
Impact:
MEDIUM-HIGH
Summary:
A phishing-delivered Hexnode management agent allowed an attacker to reinstall unauthorized ScreenConnect after the initial remote-access client was removed. Huntress investigated two alerts on the same endpoint, separated by several hours, that connected to the same attacker-controlled relay. The incident shows why removing the visible remote-control tool can leave the underlying management access intact. Proposal-themed emails referenced an organization with which the target likely had a business relationship and directed the recipient to an installer disguised as a DocuSign-related application. The package actually installed legitimate Hexnode management components, including its gateway and agent, with supporting database software. The attacker then used that management access to deploy ScreenConnect. After the service provider removed the first installation, another copy appeared and reconnected to the same relay. Huntress isolated the endpoint following the second alert and began broader remediation. The report describes abuse of legitimate administration software through social engineering; it does not identify a vulnerability in Hexnode or establish the extent of data access. It provides delivery and relay indicators, but no confirmed victim geography or campaign-wide count. First investigate unexpected management agents and enrollments whenever unauthorized remote access reappears, correlating installation history with network connections. Contain the endpoint and remove unauthorized management enrollment and attacker-created access, then revoke exposed sessions and credentials. Maintain an inventory of approved management tenants and remote-access instances, and reinforce verification of proposal and document-signing requests.
Source: https://www.huntress.com/blog/attackers-turn-mdm-into-remote-access
10/29/26
Fake Teams Invitation Enables Rippling-Delivered Remote Access
MEDIUM-HIGH
+ —
Intel Source:
Huntress
Intel Name:
Fake Teams Invitation Enables Rippling-Delivered Remote Access
Date of Scan:
10/29/26
Impact:
MEDIUM-HIGH
Summary:
An attacker used a tax-planning email and a lookalike Microsoft Teams invitation to establish unauthorized Rippling management access, then deploy ScreenConnect with SYSTEM privileges. Huntress traced the incident from a receptionist's click through endpoint enrollment evidence and remote-access installation. The linked page presented itself as a calendar and redirected through another page that appears to have facilitated enrollment into an attacker-controlled management tenant. Because the site was taken down shortly afterward, the publisher describes parts of that enrollment mechanism as an assessment. About a minute after the click, an enrollment-related registry artifact appeared. The management agent was subsequently downloaded and installed with SYSTEM permissions. Approximately 35 minutes later, the attacker used the management platform to stage and run a ScreenConnect installer that connected to an unauthorized relay and triggered an alert. Huntress determined that the activity originated from the online management agent, suggesting an account had been created to support the attack. The report does not establish a wider victim count, affected geography, or subsequent data theft. Its operational finding is a privileged deployment path created by social engineering and legitimate management functionality. Prioritize correlation of unexpected invitations, device enrollment, agent installation, and remote-access connections across endpoint and management telemetry. Isolate suspected endpoints, remove unauthorized enrollment, and disable attacker-created access before treating remote-tool removal as complete. Review approved management tenants and applications, revoke affected sessions and credentials, and reimage systems whose integrity cannot be established.
Source: https://www.huntress.com/blog/attackers-turn-mdm-into-remote-access
10/29/26
CyberDakait Android Banking Fraud and SMS Theft
MEDIUM-HIGH
+ —
Intel Source:
Group-IB
Intel Name:
CyberDakait Android Banking Fraud and SMS Theft
Date of Scan:
10/29/26
Impact:
MEDIUM-HIGH
Summary:
The CyberDakait banking-fraud campaign uses coordinated calls and messages to move Indian bank customers from a fraudulent protection-plan cancellation process into Android malware installation. Group-IB identified 17,960 compromised devices across exposed collection channels and 7,611,443 intercepted messages, including authentication codes and transaction notifications. Those are aggregate campaign findings and do not establish an equal distribution across its seven malware families. The publisher observed impersonation of 11 banking institutions and two government programs. Callers claim that a paid protection plan must be deactivated, then send a phishing link that collects card details, banking credentials, and identity information while initiating a malicious application download. GitHub-hosted payloads and fake application-update screens support delivery of additional components, while battery-optimization prompts help maintain background execution. Some analyzed chains also deploy a cryptocurrency miner. Group-IB distinguishes seven families by their communication protocols, database structures, and message formats; shared packaging and themes do not prove that every family has one developer or operator. The report also documents an administrative application used to view stolen information and issue commands. Identified distribution accounts and repositories were reported to GitHub and deactivated. Banks should prioritize customer verification of protection-plan calls and rapid response to reported application installation or fraud. Use the published indicators to investigate distribution and mobile collection infrastructure, and report replacement accounts and repositories. Restrict untrusted application installation, review sensitive permissions, and promptly freeze affected banking access when compromise is suspected.
Source: https://www.group-ib.com/blog/cyberdakait-seven-android-trojans-indian-banking/

Threat Content

Shared Security Content on Sigma

Securonix Threat Labs publishes up-to-date IOCs and threat hunting queries on Sigma, allowing you to tap into a vast community of collective defense and stay ahead of emerging threat research.
securonix in github dashboard

Why Security Content Matters

Learn how Securonix is paving the way to make precise, and actionable security content a reality for our customers.