User and Entity Behavior Analytics (UEBA)

VALID ACCESS. HIDDEN RISK

AI agents can operate with valid permissions and still move outside their expected purpose. Securonix connects behavior across users and entities, then extends that foundation to AI agents—so teams uncover developing risk without another investigation silo.

More context. Fewer disconnected alerts.  A clearer next move.

See The Behavior. Understand The Risk. Know What To Do Next.

Turn changes in human and machine behavior, identity, context, and intent into a prioritized risk narrative analysts can investigate with confidence.

Trust Is No Longer Human

AI agents do more than hold access. They use it.
They retrieve data, call APIs, and act using their own or inherited authority. Valid access can still move outside an agent’s expected purpose.

Static rules see a violation. Behavior sees the story.
Small changes across identity, authority, tools, data, and time can signal developing risk.

Securonix connects the evidence.
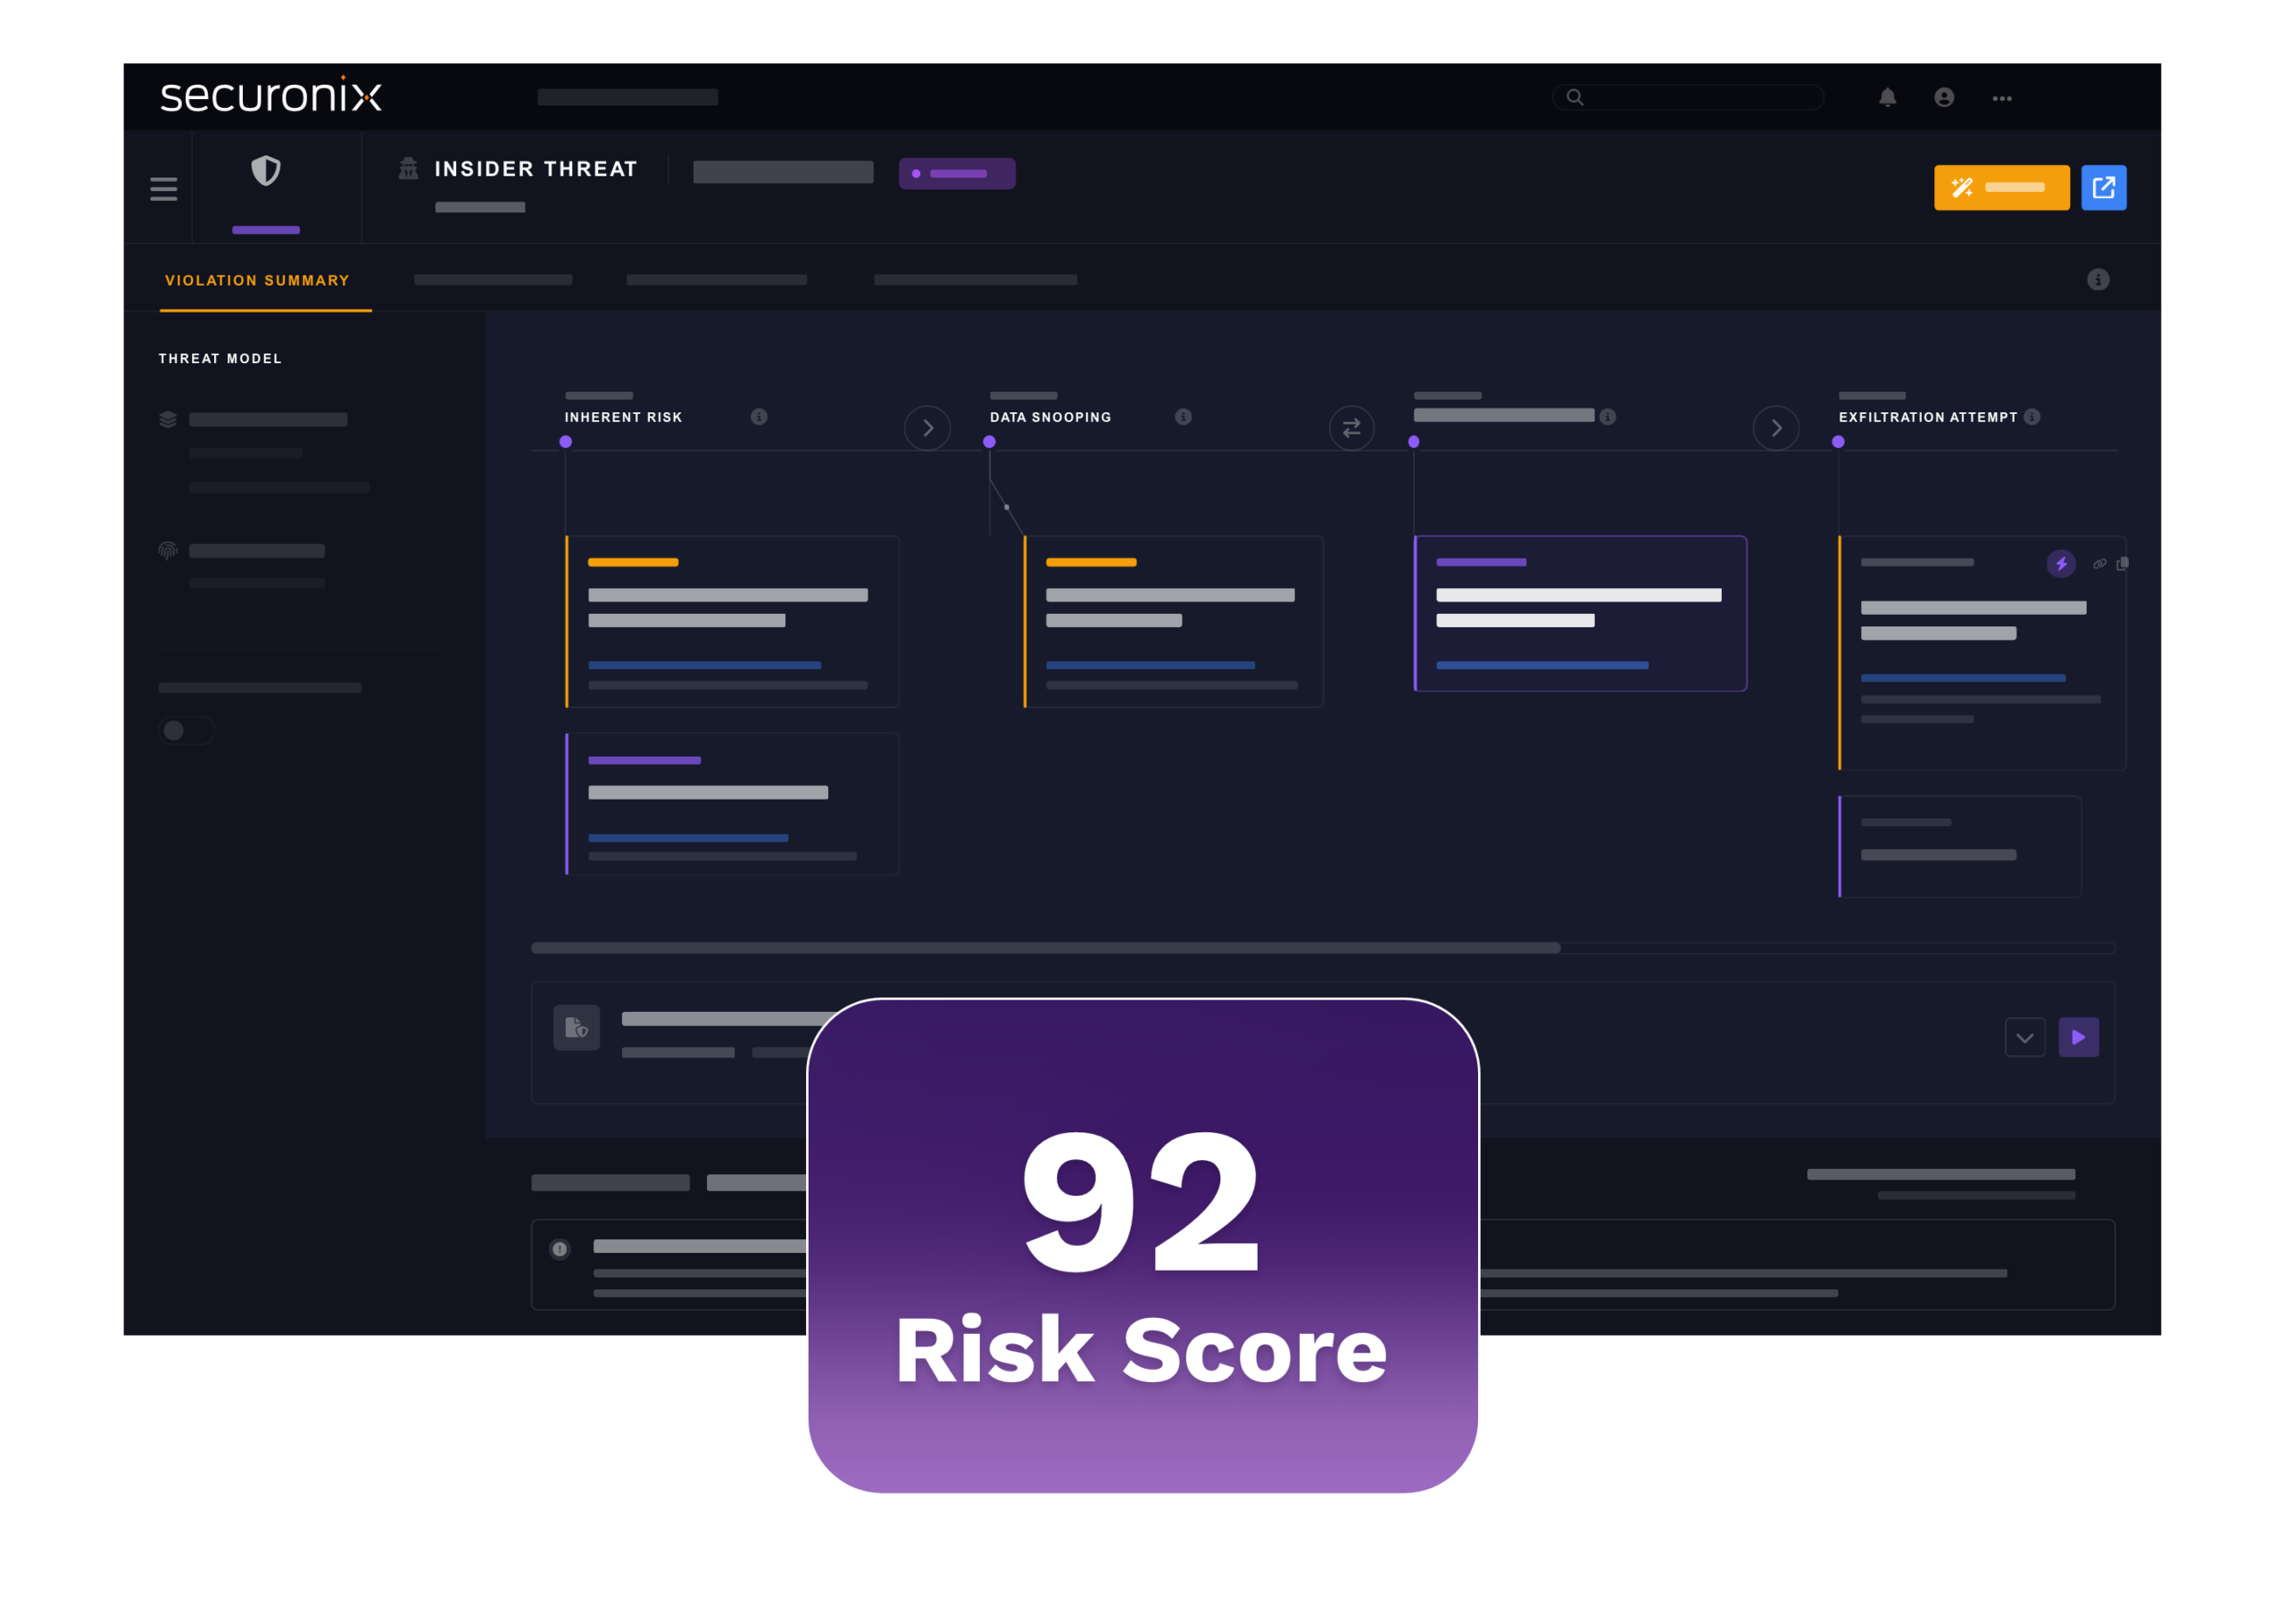
UEBA and AEBA turn related activity into one prioritized investigation, so teams can take governed action without another silo.

Detect meaningful change.
Spot rare access, abnormal volume, unexpected sequences, and unusual tool use.

Understand why it matters.
Add identity, authority, asset, data, and business context.

Act with confidence.
Prioritize the risk story and take the next governed step.

  • Detect meaningful change:  Identify rare activity, unusual access, volume spikes, suspicious sequences, privilege misuse, risky tool invocation, abnormal prompt behavior, and deviations from individual or peer-group patterns.
  • Understand why it matters:  Enrich unusual activity with identity, ownership, asset, location, threat intelligence, data sensitivity, and business context to assess likelihood and potential impact.
  • Act with greater confidence:  Connect related human and machine signals into a unified incident, prioritize the users and entities that require attention, and give analysts clear evidence for the next investigative step. 

Insider Intent Agent

The Risk Story Starts Before the Incident.

AI changed how work gets done. It changed the warning signs, too.
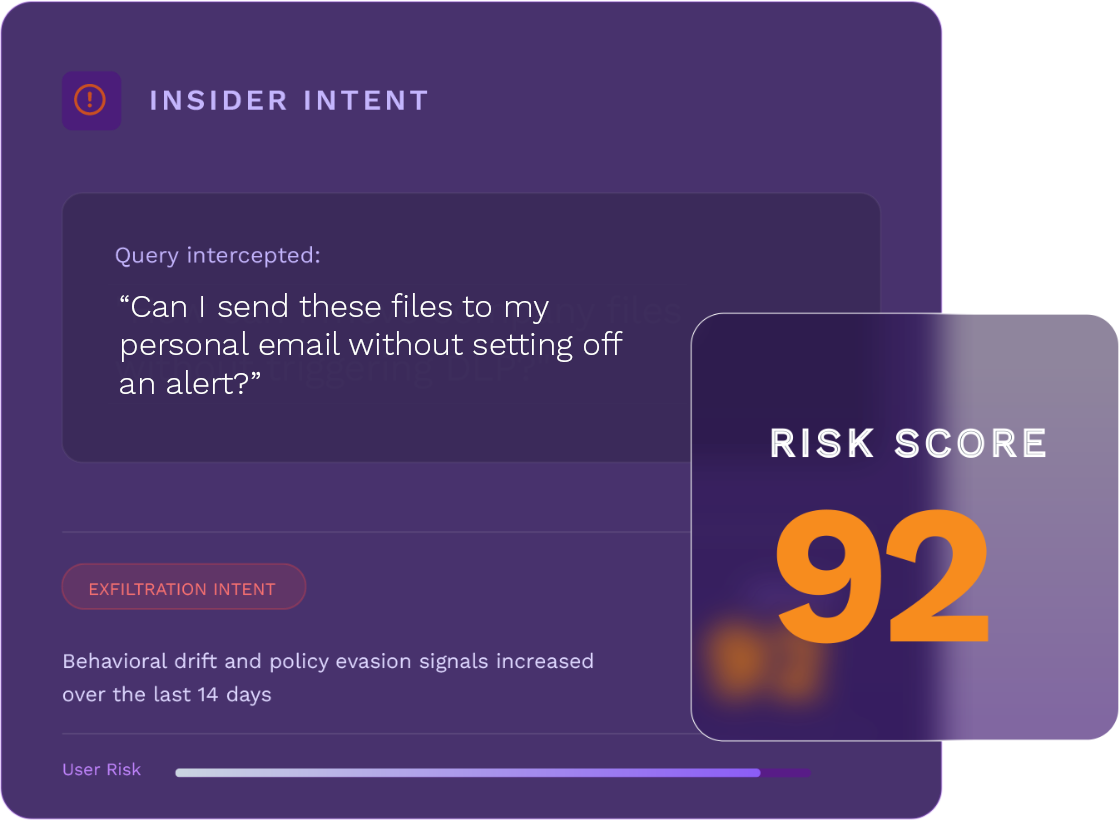
A shift in language, behavior, or AI use can reveal developing insider risk before a policy event makes it obvious.

Securonix connects the clues.
Insider Intent Agent correlates behavioral, linguistic, contextual, and AI-interaction signals with identity activity, access patterns, data movement, and asset sensitivity.

Turn early signal into the right next move.
Authorized teams get explainable, policy-aligned summaries to prioritize investigations and act with confidence.

Detect behavioral drift.
Surface unusual behavior, policy evasion, and AI-assisted sensitive activity.

See the context around the signal.
Connect communication, identity, access, and data activity in one explainable view.

Focus teams on what matters.
Give analysts the evidence to distinguish developing risk from routine noise.

Keep decisions explainable.
Provide concise summaries for analysts, investigators, and authorized stakeholders.
User, Agent, and Entity Behavior AnalyticsHow UEBA and AEBA Work

From baseline to governed action, the workflow connects activity that can look harmless when reviewed one event at a time.

See Risk Across Human and Agent Identities

Enterprise AI assistants, autonomous workflows, digital workers, and service accounts can access sensitive information and business systems, call APIs, and act on behalf of users. Their activity needs the same context and accountability applied to human users. 

Securonix AEBA extends behavioral analytics to AI agents and other non-human identities, helping teams identify unusual activity, suspicious human-to-agent interactions, risky tool use, abnormal prompts, unauthorized AI adoption, and potential misuse or compromise. 

  • See agent behavior in context  Monitor changes in agent access, tool use, application activity, API calls, and sensitive-data interactions.
  • Connect people and agents  Correlate human-to-agent activity, prompts, identity context, and downstream actions to reveal risk across the interaction.
  • Prioritize meaningful deviations  Distinguish expected automation from unsafe or policy-evading behavior so analysts can focus on what requires review. 

Investigate Insider Risk With Appropriate Governance

Insider-risk investigations can involve sensitive employee, identity, communication, and business data. Security teams need to move quickly without sacrificing privacy, oversight, or procedural control.

  • Privacy-aware controls
    Use data masking and filtering, role-based access, and approval-based unmasking to protect sensitive information. 
  • Auditable decisions
    Maintain investigation activity, decision trails, escalation policies, and human approval controls. 
  • Controlled collaboration
    Support consistent, defensible cases across security, HR, legal, and compliance.

Turn Behavioral Signals Into Operational Outcomes

Give analysts and authorized stakeholders a more complete, explainable risk picture while reducing the effort required to reach a decision.

Key UEBA and AEBA use cases

Apply behavior, identity, intent, agent activity, and context to risks that are difficult to detect with isolated rules and alerts.

Insider threat detection

Identify behavioral and intent signals associated with negligent, compromised, or malicious insiders before they create material impact.

Privilege and data misuse

Connect unusual access, privilege abuse, data movement, communication activity, and behavioral change to reveal potential exfiltration or policy evasion.

AI risk and data leakage

Identify risky prompts, sensitive-data use, abnormal tool invocation, policy evasion, and unusual behavior within supported AI-assisted workflows.

Non-human identity risk

Monitor behavioral change involving service accounts, autonomous agents, digital workers, and other machine identities.

Identity threat detection and response

Detect credential abuse, abnormal access, suspicious authentication, impossible travel, privilege escalation, lateral movement, and account misuse.

Low-and-slow and multi-stage threats

Correlate activity across systems and time to expose developing risk that isolated alerts and static rules can miss.

Compliance monitoring and audit readiness

Use explainable detections, masking, approval controls, audit trails, and governed workflows to support defensible investigations and oversight requirements.

Deploy behavioral analytics around your security strategy

Deploy combined UEBA and AEBA within Securonix Unified Defense SIEM, or extend the behavior-driven detection available to Microsoft Sentinel with Securonix Threat Analytics.

Behavior across users agents and entities in one operating model

Securonix Unified Defense SIEM

Deploy UEBA and AEBA as behavior-first, identity-centric capabilities embedded within Unified Defense SIEM and extended by the Insider Intent Agent and Agentic Mesh.

  • Unified telemetry, identity, behavior, intent, agent activity, and business context
  • Cross-domain detection, threat-chain correlation, and retrospective analysis
  • Workflow-embedded investigation and response
  • Governed AI with explainability, auditability, and human oversight
  • Clear risk and operational visibility for the SOC and executives 

More behavioral context without replacing the SIEM

Securonix Threat Analytics for Microsoft Sentinel

Securonix applies behavior-driven analytics, UEBA, advanced correlation, entity context, dynamic risk scoring, and continuously maintained detection content to telemetry already available in Sentinel.

  • No SIEM replacement
  • No disconnected analyst experience
  • No duplicate telemetry pipeline
  • No additional endpoint agents
  • More than 2,400 continuously maintained detections

Detect earlier across people and agents

Behavioral analytics for modern security operations

Discover how Securonix UEBA and AEBA can help your team find insider, identity, and agent risk earlier, reduce investigation drag, and make more consistent, defensible decisions. 

Request a Demo
Request a Demo

By clicking submit you agree to our Privacy Policy.